
Understanding Data Recovery for an External HDD With Encryption
In this article
An encrypted external hard drive acts as a secure digital vault for your data. While a standard external drive is like an open file cabinet - accessible to anyone who possesses it - an encrypted drive locks every file. Without the correct decryption key, your data is unreadable, a concept known as ciphertext.
This fundamental security feature ensures that if your drive is lost or stolen, your information remains confidential and secure.
How Encryption Protects Your Data

At its core, an encrypted external HDD implements a layer of security that standard drives lack. A regular drive stores files in their native format, meaning anyone who connects it to a computer can view the contents.
An encrypted drive uses a sophisticated algorithm - a complex set of mathematical rules - to scramble data into ciphertext. To convert that ciphertext back into usable files, the correct key is required. This key is typically a password but can also be a dedicated recovery key.
Without that key, the data on the drive is useless to an unauthorized party.
The Importance of Encryption for Portable Drives
External drives are portable, which makes them susceptible to being lost, misplaced, or stolen. For users transporting sensitive information, this convenience introduces significant risk. Encryption serves as an essential safeguard against these real-world scenarios.
- For Professionals: It protects client data, financial records, and intellectual property from unauthorized access.
- For Personal Use: It secures tax documents, medical records, and other private information from identity thieves.
- For Everyone: It keeps personal photos and videos private, ensuring that even if the physical drive is lost, the memories are not exposed.
The adoption of this technology is growing. The global market for encrypted hard drives is projected to increase from USD 3.2 billion in 2026 to USD 5.93 billion by 2033. This growth, detailed in a Straits Research report, underscores the critical role of data protection.
How Encryption Impacts Data Recovery
When an encrypted drive fails due to a mechanical issue like a head crash or motor failure, the data is not only physically inaccessible but also locked behind a layer of security.
This dual challenge is why professional lab services are necessary for these cases. The recovery process involves two distinct stages. First, our engineers must physically repair or stabilize the drive in a certified clean-room environment to create a complete, stable clone of the raw, encrypted data. Only after a perfect image is secured can the client's password be used to unlock and decrypt the recovered files.
Hardware vs. Software Encryption: A Technical Comparison
When choosing how to encrypt an external hard drive, the primary decision is between hardware-based and software-based encryption. Both methods secure your data, but they operate differently, with distinct implications for performance, security, and the data recovery process.
Understanding these differences is crucial, as the choice affects drive speed, security integrity, and the technical approach required for recovery if a failure occurs.
What Is Hardware Encryption?
Hardware encryption utilizes a dedicated cryptographic processor built directly into the external drive's circuit board. This specialized chip manages all encryption and decryption operations independently of the host computer.
Because a dedicated processor handles the cryptographic load, the computer's CPU is not burdened. This results in faster performance and makes the encryption process seamless and independent of the operating system. Once unlocked with a password, the drive functions like a standard device but with a persistent, high-performance security layer.
The self-contained nature of this technology is driving its market growth. The hardware encryption market is projected to expand from USD 659.0 billion in 2025 to USD 6,243.1 billion by 2034, with external HDDs being a key segment. You can review the market trends in IMARC Group's full analysis.
The Software Encryption Alternative
Software encryption relies on an application or an operating system feature to secure files. Common examples include BitLocker To Go for Windows and FileVault for macOS.
Instead of a dedicated chip on the drive, this method uses the host computer's central processing unit (CPU) to perform the cryptographic calculations. Data is encrypted by the computer before it is written to the external drive.
While software encryption is widely accessible and often free, its performance is directly tied to the host computer's processing power. Older or less powerful systems may experience noticeable slowdowns during large file transfers as the CPU juggles its normal tasks with the demands of encryption.
A Side-by-Side Comparison
The choice between hardware and software encryption involves a series of trade-offs. The optimal solution depends on specific needs, such as the sensitivity of the data and the user's workflow.
Hardware Encryption vs Software Encryption at a Glance
This table outlines the key differences to help you determine which approach aligns with your requirements.
| Feature | Hardware Encryption (e.g., SEDs) | Software Encryption (e.g., BitLocker, VeraCrypt) |
|---|---|---|
| Performance | Faster, due to a dedicated cryptographic processor. No impact on host computer CPU. | Slower, as it relies on the host computer's CPU. Performance may lag on less powerful systems. |
| Security | Generally higher. The encryption key is managed on the drive, making it more resistant to OS-level attacks like keyloggers. | Secure, but potentially vulnerable if the host computer is compromised with malware. |
| Compatibility | OS-agnostic. Operates independently of the operating system (Windows, macOS, Linux). | Often OS-dependent. A BitLocker-encrypted drive requires third-party software to be accessed on macOS. |
| Cost | Typically more expensive due to the inclusion of specialized hardware components. | Often free. Included with the operating system or available as free third-party software. |
Ultimately, if maximum performance and robust, OS-independent security are priorities, a drive with hardware encryption is the superior choice. For cost-effective, everyday protection on a single operating system, software encryption is a reliable and practical solution.
A Look at Common Encryption Technologies
Selecting an encrypted external hard drive involves choosing a specific security technology to safeguard your files. Understanding these technologies is important for appreciating both the strength of the protection and the complexities involved in data recovery.
While the field of cryptography is vast, a few key standards dominate the consumer and enterprise markets.
AES-256: The Industry Standard
Nearly all modern encrypted devices utilize the Advanced Encryption Standard (AES). The most common implementation is AES-256, which refers to its 256-bit key length.
An encryption key's length determines its complexity. The number of possible combinations for a 256-bit key is astronomical, making it computationally infeasible to break with current technology. It would take the world's most powerful supercomputers billions of years to guess the key through a brute-force attack. For this reason, AES-256 is trusted by governments, financial institutions, and security-conscious organizations worldwide.
This is precisely why, during a data recovery case, our laboratory's role is not to "break" the encryption - that is impossible. Our engineers focus on meticulously repairing the drive's physical or logical damage to achieve a stable state where you can unlock it with your password.
Common Software-Based Encryption Tools
Many users begin with software encryption tools integrated into their operating systems due to their accessibility and ease of use.
BitLocker To Go (Windows): This is Microsoft's native solution for encrypting removable drives. It is integrated into professional versions of Windows and allows users to secure a drive with a password. It also generates a recovery key - a long numerical password that must be saved in a safe, separate location. This key is the only alternative for access if the primary password is forgotten.
FileVault (macOS): For Mac users, FileVault provides native encryption for external drives. It integrates with the Apple ecosystem, often using the user's login password or iCloud account for recovery purposes.
Hardware-Level Security: TCG Opal and SEDs
For the highest level of security and performance, hardware-based encryption is the standard. Self-Encrypting Drives (SEDs) are storage devices with encryption capabilities built directly into the drive's controller.
These drives encrypt all data by default, and the process is transparent to the user with no performance degradation. The most common standard governing these drives is TCG Opal 2.0. An Opal-compliant drive provides strong, always-on protection that operates independently of the host computer's operating system.
According to a market analysis, the hardware encryption market is projected to reach USD 430.22 million by 2031. The report also confirms that the Advanced Encryption Standard (AES) maintains a dominant 61.75% market share. You can explore more about these technologies in the hardware encryption technologies on Mordor Intelligence. These figures highlight the industry's reliance on these proven standards for data protection.
How Drive Failure Impacts Encrypted Data Recovery
A common question from clients is: "If my encrypted drive fails, is the data lost forever?"
The answer is typically no, but the failure introduces significant complexity. Encryption adds a formidable security layer, but it does not make data recovery impossible.
It does, however, transform the recovery into a two-stage process. First, our lab must address the physical, firmware, or logical failure of the drive. Only after we have successfully cloned the raw, encrypted data can we proceed to the decryption stage using your credentials.
The Two-Fold Challenge of Encrypted Drive Failure
When an encrypted drive fails, we must overcome two distinct obstacles: the physical or logical damage and the cryptographic lock.
Consider the data as being stored inside a high-security vault (encryption) that has just been damaged in an earthquake (the drive failure). Before the combination can be used, the vault must be excavated from the rubble and its locking mechanism repaired. This is analogous to our data recovery process.
This is also why data recovery software is ineffective and dangerous for these cases. Software tools are designed to operate on healthy hardware.
Attempting to run DIY software on a physically failing encrypted drive is one of the most common ways a recoverable situation becomes a permanent data loss. The software cannot diagnose the physical distress and will force the drive to read damaged areas, which can cause further degradation of the magnetic platters, destroying the raw encrypted data before a professional lab can safely image it.
How Different Failure Types Complicate Recovery
The type of failure dictates the recovery strategy. Each failure mode interacts with the encryption layer differently and requires specialized lab-level tools and expertise.
Logical Failures
This is the most straightforward recovery scenario. In a logical failure, the drive's hardware is intact, but the data structures, such as the file system, have become corrupted. This can happen from improper ejection or a software malfunction.
- Failure Symptoms: The drive is detected by the computer but prompts to be formatted, displays an incorrect capacity, or appears as a "RAW" partition.
- Recovery Method: We use professional imaging hardware to create a perfect, sector-by-sector clone of the drive. This bypasses the operating system's misinterpretation of the data. Once a stable image is created, your password or BitLocker key can be used to unlock the volume, allowing us to reconstruct the file system and extract your data.
Firmware Corruption
The firmware is the drive's internal operating system. If it becomes corrupted, the drive can become non-functional, even if the physical components are undamaged.
- Failure Symptoms: The drive may spin up but is not detected by the computer, or it may be identified with an incorrect model name or 0GB capacity.
- Recovery Method: This requires firmware-level tools like the PC-3000. Our engineers can directly access the drive's protected service area to repair the corrupted firmware modules. Once the drive can communicate correctly, we can proceed with imaging the encrypted data.
Mechanical and Electrical Failures
These are the most severe failures, including head crashes, motor seizures, or damage to the printed circuit board (PCB).
- Failure Symptoms: Audible clicking, grinding, or beeping sounds are classic indicators of mechanical failure. A completely dead drive with no power or spin activity usually points to an electrical issue.
- Recovery Method: This work must be performed in a certified clean-room environment. Opening a hard drive in a normal environment will cause contamination and permanent data loss. Our engineers perform micro-soldering or physically transplant components, such as read/write heads or motors, from a compatible donor drive. The objective is to stabilize the drive long enough to create one complete image of the platters.
The MDRepairs Lab-Level Approach
MDRepairs is a nationwide mail-in data recovery service specializing in these complex cases. Our process for a failing encrypted external HDD is methodical and prioritizes data safety.
- Professional Diagnostics: We begin with a risk-free quote to determine the exact nature of the failure - logical, firmware, or physical.
- Physical Repair: If required, all repairs are performed in a Class 100 certified clean room.
- Advanced Imaging: Using specialized hardware, we create a complete, sector-by-sector clone of the drive, capturing the raw encrypted data.
- Client-Led Decryption: We only proceed to decryption after securing a stable image of your data. At this stage, you provide the password or recovery key, which we use to decrypt the data on our secure systems. Your credentials are handled with strict confidentiality and are never stored.
This professional process allows us to safely navigate hardware failures and recover your encrypted data. If you are experiencing drive failure, you can learn more about our professional evaluation and services for data recovery in California and throughout the United States.
What to Do Immediately if Your Encrypted Drive Fails
When an encrypted drive shows signs of failure, the initial moments are critical. The actions you take - or avoid - can determine the success of a professional recovery effort.
The most important rule is to power down the device immediately. Continuing to operate a failing drive can cause irreversible damage.
Stop and Power Down
The impulse to try reconnecting the drive or running a disk utility is strong, but these actions are extremely risky for a physically failing device.
- Clicking or Grinding Sounds: These noises indicate a severe mechanical failure, likely involving the read/write heads. Every second the drive remains powered on, the heads can be physically scraping the magnetic coating off the platters, destroying the encrypted data stored there.
- Repeatedly Plugging It In: Each power-on cycle forces the drive through a startup sequence that can place stress on failing components, potentially causing a catastrophic failure.
- Running Disk Utilities: Tools like
chkdskor Disk Utility's First Aid are designed for logical errors on healthy hardware. On a failing drive, they can misinterpret bad sectors, get stuck in a loop, and cause fatal stress to the mechanical components.
The professional recovery process is sequenced to protect your data. Decryption is the final step, performed only after a complete, stable image of the raw data has been created from the damaged hardware.
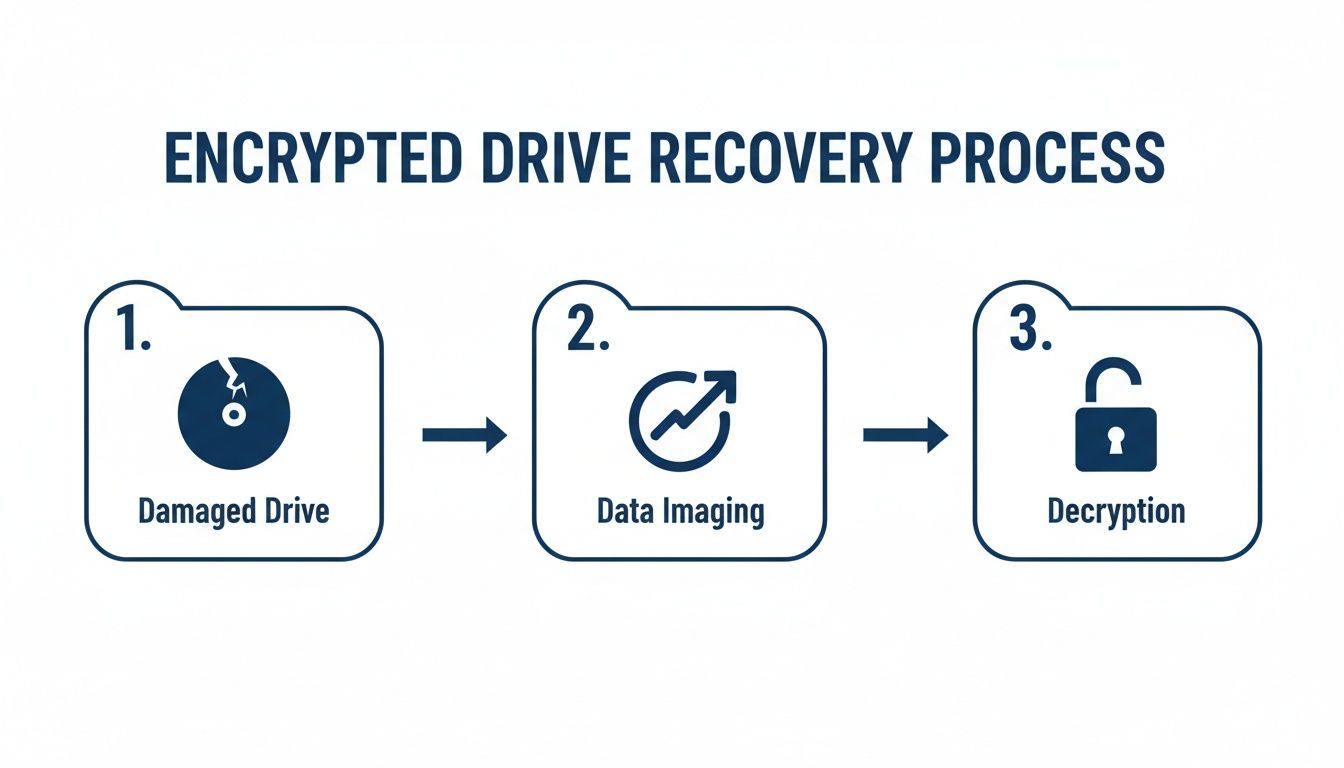
As this illustrates, decryption is only possible after a safe and complete image of your data has been captured.
The Professional Recovery Process
Once the drive is powered down, the next step is to have it evaluated by a professional data recovery lab. MDRepairs offers a nationwide mail-in service designed for complex encrypted drive failures.
To complete the recovery, we will need certain information, but only after your data has been safely imaged.
What We'll Need for Decryption:
- The Password: The primary passphrase used to unlock the drive.
- The BitLocker Recovery Key: A 48-digit numerical key that serves as a master key for BitLocker-encrypted volumes.
- The FileVault Recovery Key: The equivalent key for drives encrypted on macOS.
This information is highly sensitive. Your password or recovery key is handled with strict security protocols and is only requested during the final decryption phase, after a stable clone of your drive is secured. All our services are covered by a no data, no charge policy, meaning there is no financial risk for the evaluation. You can learn more about how we manage these cases in our overview of the Texas data recovery process.
Best Practices for Protecting Your Encrypted Data
The most effective data recovery strategy is one that is never needed. Using an encrypted external HDD is an excellent measure for data security, but long-term data integrity depends on disciplined practices.
Adopting these strategies provides a robust defense against hardware failure, data corruption, and human error.
Secure Your Keys Above All Else
This is the most critical rule: your password and recovery key are irreplaceable. If they are lost, the data is permanently inaccessible. No data recovery laboratory, including MDRepairs, can bypass modern AES-256 encryption. Our role is to repair the physical device so that you can unlock it; we cannot break the cryptographic lock itself.
It is mandatory to store your credentials in a separate, secure location. Never store the only copy of your password or recovery key on the encrypted drive. This is analogous to locking the only key to a safe inside the safe itself.
Recommended methods for managing keys include:
- Password Manager: Use a reputable password manager to securely store both the password and the full recovery key.
- Physical Copy: Print the recovery key and store it in a secure physical location, such as a fireproof safe or a bank safety deposit box.
- Trusted Contact: As part of a digital estate plan, consider sharing credentials with a trusted legal or family representative.
Implement the 3-2-1 Backup Rule
Encryption protects data from unauthorized access, but it does not protect against drive failure, file corruption, or accidental deletion. That is the role of backups. The industry best practice is the 3-2-1 rule.
- Three Copies: Maintain at least three copies of your important data.
- Two Media Types: Store these copies on at least two different types of storage media (e.g., your encrypted external HDD and a cloud service).
- One Off-Site Copy: Keep at least one copy in a separate physical location to protect against local disasters like fire, flood, or theft.
For businesses managing sensitive data, frameworks like the SOC 2 encryption requirements provide guidance on implementing robust data protection strategies.
Practice Safe Handling and Ejection
Physical handling and proper digital disconnection are simple but effective preventative measures.
- Always Safely Eject: Never disconnect the drive by simply unplugging the USB cable. Use the "Safely Remove Hardware" function in your operating system. This ensures all write operations are completed and prevents file system corruption.
- Avoid Physical Shocks: An HDD contains sensitive moving parts, including spinning platters and read/write heads. Dropping or jarring the drive can cause severe mechanical damage.
- Use High-Quality Cables: A faulty USB cable can cause intermittent connections, leading to data corruption. Use a high-quality, reliable cable.
Your Top Questions About Encrypted HDD Recovery Answered
When an encrypted external drive fails, it is natural to have questions about the intersection of hardware failure and data security. Here are answers to some of the most common concerns we address in our lab.
Can Data Be Recovered if I Forgot My Encryption Password?
Unfortunately, no. If the password and the recovery key are both lost, the data is irretrievably lost.
Encryption standards like AES-256 are designed to be unbreakable. There are no "backdoors" or technical workarounds; their security relies on this principle.
Our role as a data recovery lab is to repair the physical or logical damage to the drive to create a perfect clone. After that, your credentials are the only way to decrypt the data. The password or recovery key must be provided by you for the final step.
Is the Data Recovery Process Secure for Sensitive Information?
Absolutely. Our entire process is built on a foundation of security and confidentiality.
We request your password only at the final stage of the process, after we have successfully imaged the drive and are prepared to extract the files.
Once recovery is complete, your decrypted data can be transferred to a new encrypted drive, ensuring it remains secure during transit back to you. This end-to-end security is a standard part of our service. You can learn more in our guide to data recovery services in Florida.
Will Running Recovery Software Harm My Encrypted Drive?
Using DIY recovery software on a physically failing drive is extremely risky. If the drive is making unusual noises (clicking, grinding) or is not being detected properly, running any software on it can cause further damage.
These tools are designed for logical issues on healthy hardware and cannot manage failing mechanical components.
For a physically failing encrypted drive, the risk is severe. Software can stress the failing components, potentially destroying the data before it can be professionally imaged. It is critical to power it down and seek a professional evaluation.
If your encrypted drive has failed, the next step is a professional, risk-free quote. MDRepairs offers nationwide mail-in diagnostics to safely determine the exact cause of failure and the best path to recovery.
How MDrepairs can help
Real cases like this come through our New Jersey lab every week. If you are dealing with one now, start here.
- Hard Drive Data Recovery Mechanical, firmware and logical HDD recovery on every brand. Learn more
- Data Recovery Services Every device and failure type, recovered in our New Jersey lab. Learn more
- SSD Data Recovery Controller, NAND and firmware recovery for SATA, M.2 and NVMe SSDs. Learn more
- Mail-In Data Recovery Free insured shipping both ways, anywhere in the US. Learn more


